
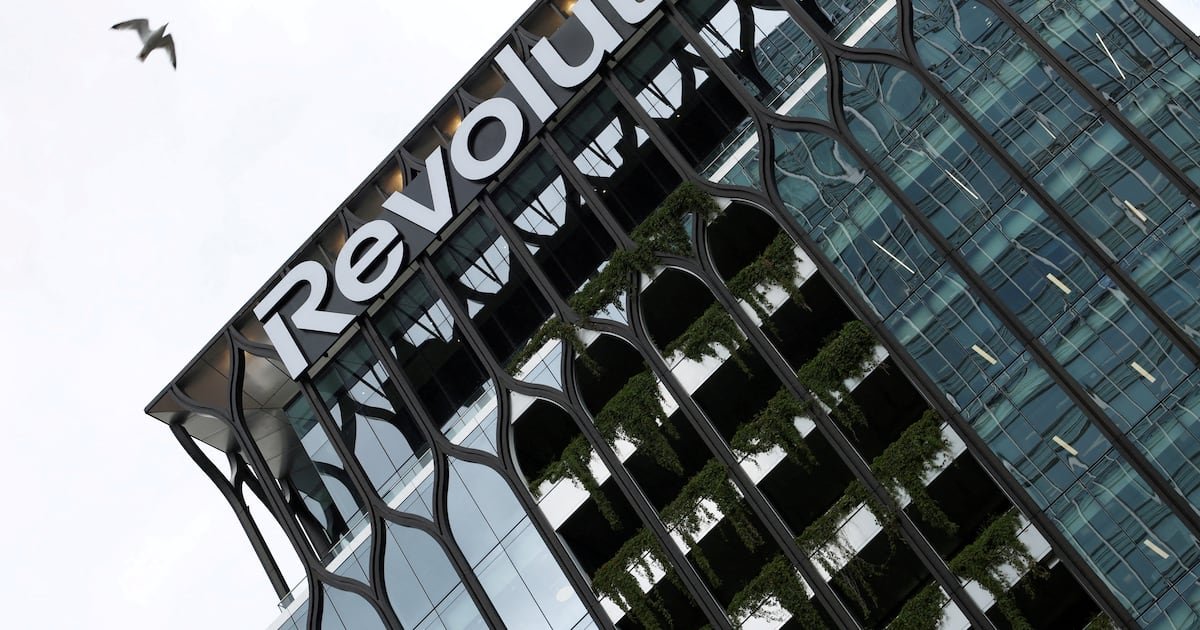
Cybersecurity experts are warning that significant lessons must be drawn from a recent incident where the digital banking platform Revolut was tricked into handing over sensitive customer data to hackers.
The UK-based fintech company, which serves more than 80 million customers, confirmed that an individual impersonating an Italian government regulatortos, account statements, transaction histories, and other personal data
Some reports indicate that the hackers are currently leaking this information and demanding a ransom from Revolut to prevent further data exposure.
Revolut has not yet responded to requests for comment.
<a s systems, the attackers asked for the data and the bank sent it,” said Ivan Milenkovic, vice president for cyber risk security firm Qualys.
Mr. Milenkovic noted that while the criminals compromised an Italian government email system to pose as law enforcement, they also exploited human nature.
“The weak point was the [Revolut] desk that answers police requests and how much it trusts a government domain,” he said. He added that the nature of the stolen information—which reportedly includes passports, driving licenses, and verification selfies—is particularly concerning. “You can reset a password in a minute but you can’t reset your face.”
Santiago Pontiroli, a threat-intelligence research lead at Acronis, reflected on how an initial data breach evolved into an extortion attempt, with the hacker believed to have requested approximately $3 million in blockchain-based cryptocurrency.
Although Revolut stated it had received no “direct demand”, Mr. Pontiroli said “the public countdown increased the pressure on the bank and affected customers”.
He added that for too long, this form of phishing has been dismissed as a threat only to older or less tech-savvy individuals.
“Evidence demonstrates this stereotype is outdated and anyone can be deceived when an approach fits the context and arrives through a channel they already trust,” Mr. Pontiroli said.
Regarding the Revolut incident, he noted that “the apparent targets of the deception were employees responsible for handling official information requests, not elderly or inexperienced consumers”.
Art Gilliland, chief executive of Delinea, which specializes in digital data and identity security, argued that it is counterproductive to frame such attacks as merely a failure of technical literacy.
“The request … carried strong signals of legitimacy and authority that many experienced professionals could reasonably find convincing,” he said.
Mr. Gilliland pointed out that because reports suggest roughly 650 Revolut customers were impacted, the goal was likely “not to collect as much data as possible, but to identify individuals whose information could provide the greatest leverage”.
He stated that even the most experienced cybersecurity professionals and organizations can learn from this incident.
“Organisations cannot make employees, no matter how tech savvy they may be, the final line of defence,” he said. “A legitimate email domain should never be sufficient proof on its own and sensitive requests need independent verification, appropriate approval and controls that restrict both, who can access the information, and how much can be released.”
Similar incidents on smaller scale
Revolut is not the only entity to be targeted in this manner.
Technology, culture, and philosophy writer Joan Westenberg recently detailed a social engineering attempt disguised as a podcast that expressed interest in booking her as a guest.
“Their prep was impeccable with better interview questions than most journalists,” she posted on social media platform Threads. The individuals provided a link that asked her “to run a terminal command to install their webinar tool”, prompting her to recognize the hacking attempt and cease communication.
Ms. Westenberg said the cybercriminals continued to pressure her to proceed and later harassed her when she stopped responding. “Never, ever install custom software for a meeting or podcast,” she wrote.
Mr. Pontiroli identified this as an example of “ClickFix-style social engineering,” a tactic becoming increasingly popular among state-sponsored hackers in North Korea.
“The victim is persuaded to execute malware under the pretext of installing software or fixing a technical problem,” he said. “The screenshots and subsequent harassment also appear designed to pressure the target into ignoring their doubts.”
He added that while the tactic is not new, the rise of artificial intelligence has made it significantly easier to carry out.
“While there’s no indication that AI was used in this particular case, it’s making similar attacks cheaper, faster and easier to scale,” he said.
